Nancy Laney Has Spoken and Been Featured At
CMMC Implementer's Conference
CMMC Day
Peak Global protects defense contractors, American businesses and local governments from the cyber threats that now shape national security.
CMMC/NIST 800-171/Managed IT/Cybersecurity/Public Safety Systems
Most breaches and most failed assessments start the same way: leadership hands security to IT and moves on. Only a third of a CMMC program is technical. The rest is policy, training, roles and accountability, and that work belongs to the people who run the organization.
Nancy Laney spent 30 years leading regulated change in hospitals and county government. Peak brings that discipline to every client, with a plan in numbered steps and dated evidence behind every claim.
Our Philosophy →
Compliance and security work stalls when it lands on someone who already has a full time job. We take the paperwork, the monitoring and the follow through off your team.
We map your systems, data and contracts, then score you against the standard you have to meet. You get the real number.
We put the controls in place and write the policies, plans and evidence that prove them. Every claim maps to a dated document.
Compliance drifts the day after an assessment. We monitor, update the paperwork and brief leadership so your record stays accurate.
Managed IT and cybersecurity for American companies. We lock down the networks, endpoints and backups that stand between your business and a ransom demand, and we keep your designs and client data in your hands.
Enter ITSS →
CMMC and NIST 800-171 compliance for defense contractors. We write and maintain the policies, the SSP and the evidence your assessor reads, so the SPRS score you sign is a true one. Our team includes Certified CMMC Assessors.
Enter Complyance →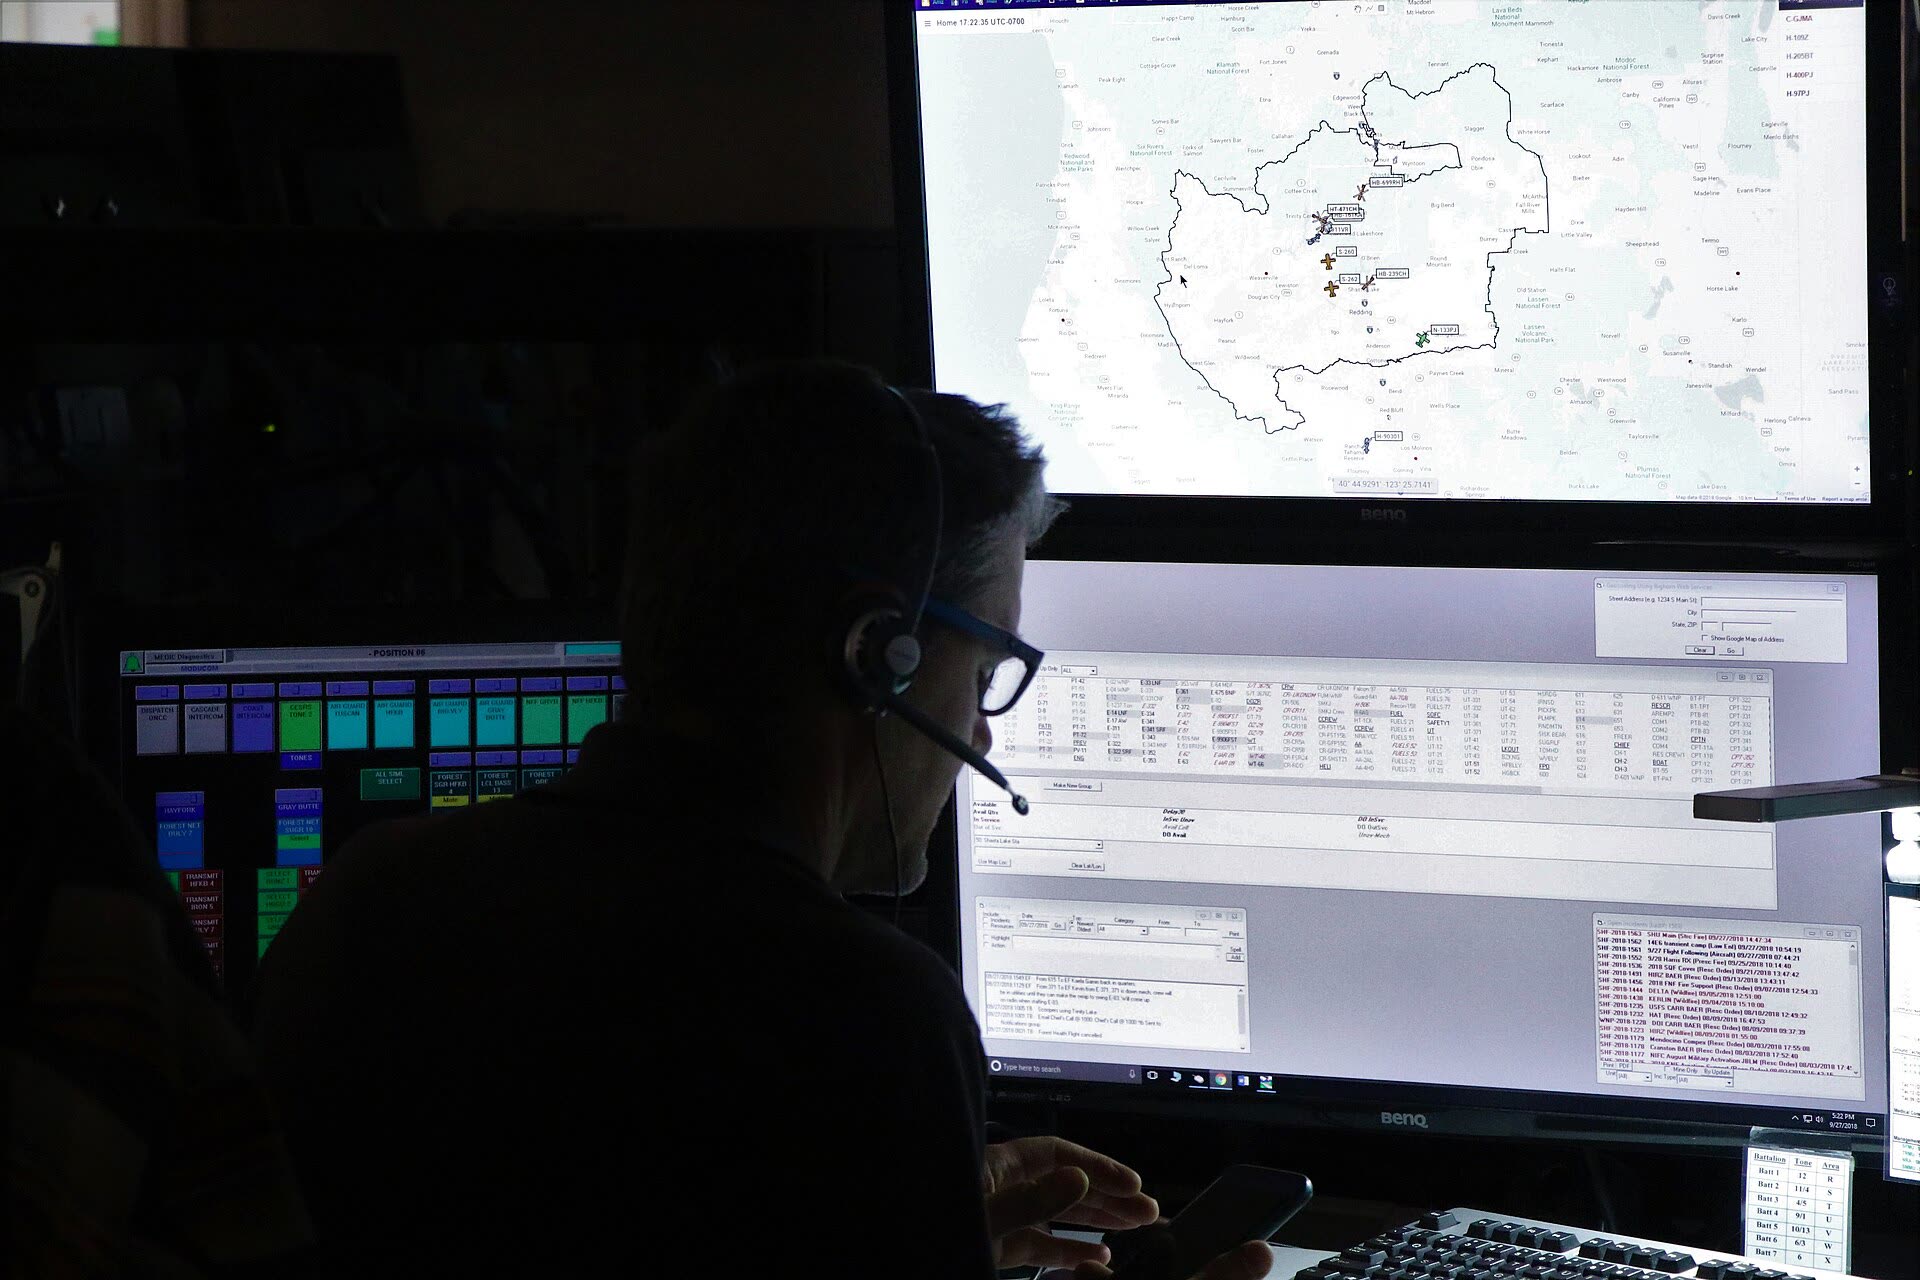
IT, cybersecurity and emergency communications for local government. Counties run the 911 radios, records and networks that residents and nearby military installations depend on. We keep them secure and running.
Enter Gov →
The highest point, reached on purpose. In our work, it's the moment every system you run is protected and every claim you make can be proven.
Nancy has spent more than 30 years finishing the projects other people called impossible.
She led IT for 4 hospitals, built a health system's HIPAA security program from the first day of the law, and secured more than $20M in public safety grants for an Oregon county. She founded Peak to carry the compliance load for the small and mid sized firms that build America's defense, and she teaches their leaders that CMMC is organizational change they have to own.
Meet Nancy Book Her to Speak